
Application Mapping(PART-2)
Hidden Content Discovery & Intelligent Prediction
1. Conceptual Blueprint: Why Hidden Content Exists
Leaving hidden files on a server is similar to having unmapped maintenance rooms in a physical building. Standard users navigate exclusively through the front door (the UI), whereas penetration testers actively search for unlinked rear entrances.
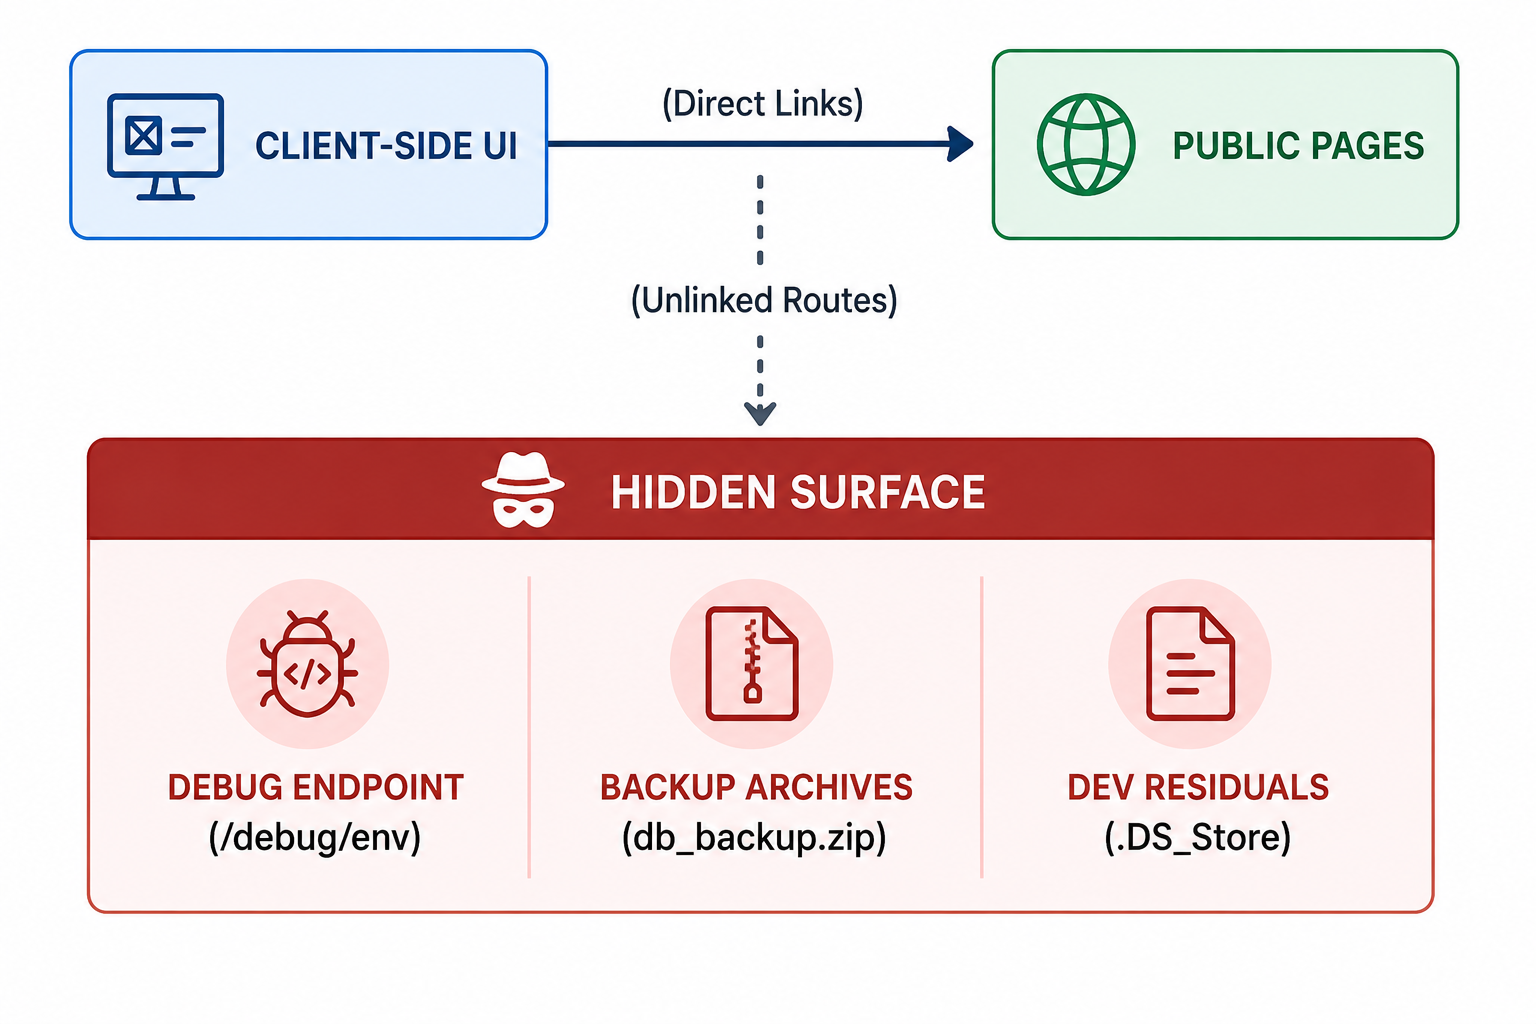
Root Causes Checklist:
Developer Artifacts: Code editor auto-save files and temporary swap files (
.tmp,~).Environment Drift: Debug mode flags left enabled in production environments.
Access Control Oversight: Functionality hidden purely via UI elements (e.g., CSS
display:none) without backend authorization checks.Legacy Leftovers: Deprecated API versions (
/v1/) remaining active after newer releases (/v2/).
2. High-Value Targets (Cheat Sheet)
| Target Category | What It Exposes | High-Risk Examples |
|---|---|---|
| Source Leaks | Raw application source code, embedded credentials | config.php.bak, index.php.old, app.src |
| System Archives | Full codebase snapshots, SQL dumps, SSL certificates | backup.tar.gz, db_dump.sql, site-v1.zip |
| Sensitive Logs | Active session tokens, internal parameters, user activity | debug.log, access.log, trace.axd |
| OS Leftovers | Directory structures, system file listings | .DS_Store (macOS), Thumbs.db (Windows) |
| Config Archives | Database connection strings, API keys, environment settings | web.config, settings.json, .env |
3. Decoding HTTP Status Codes (Pen-Tester Lens)
During automated discovery, HTTP status codes often carry tactical meanings that differ from standard RFC definitions:
200 OK: Direct Hit (Verify response body size and content to filter out soft 404s).
302 / 307 Redirect:
Redirecting to
/login\(\rightarrow\) Target exists, but requires authentication.Redirecting to
/error\(\rightarrow\) Target is likely invalid or nonexistent.
401 Unauthorized: Resource exists; requires valid user credentials.
403 Forbidden: Directory listing disabled or access restricted — Strong indicator that the path exists.
500 Internal Error: Required parameter or header missing, but the application attempted processing — Resource exists.
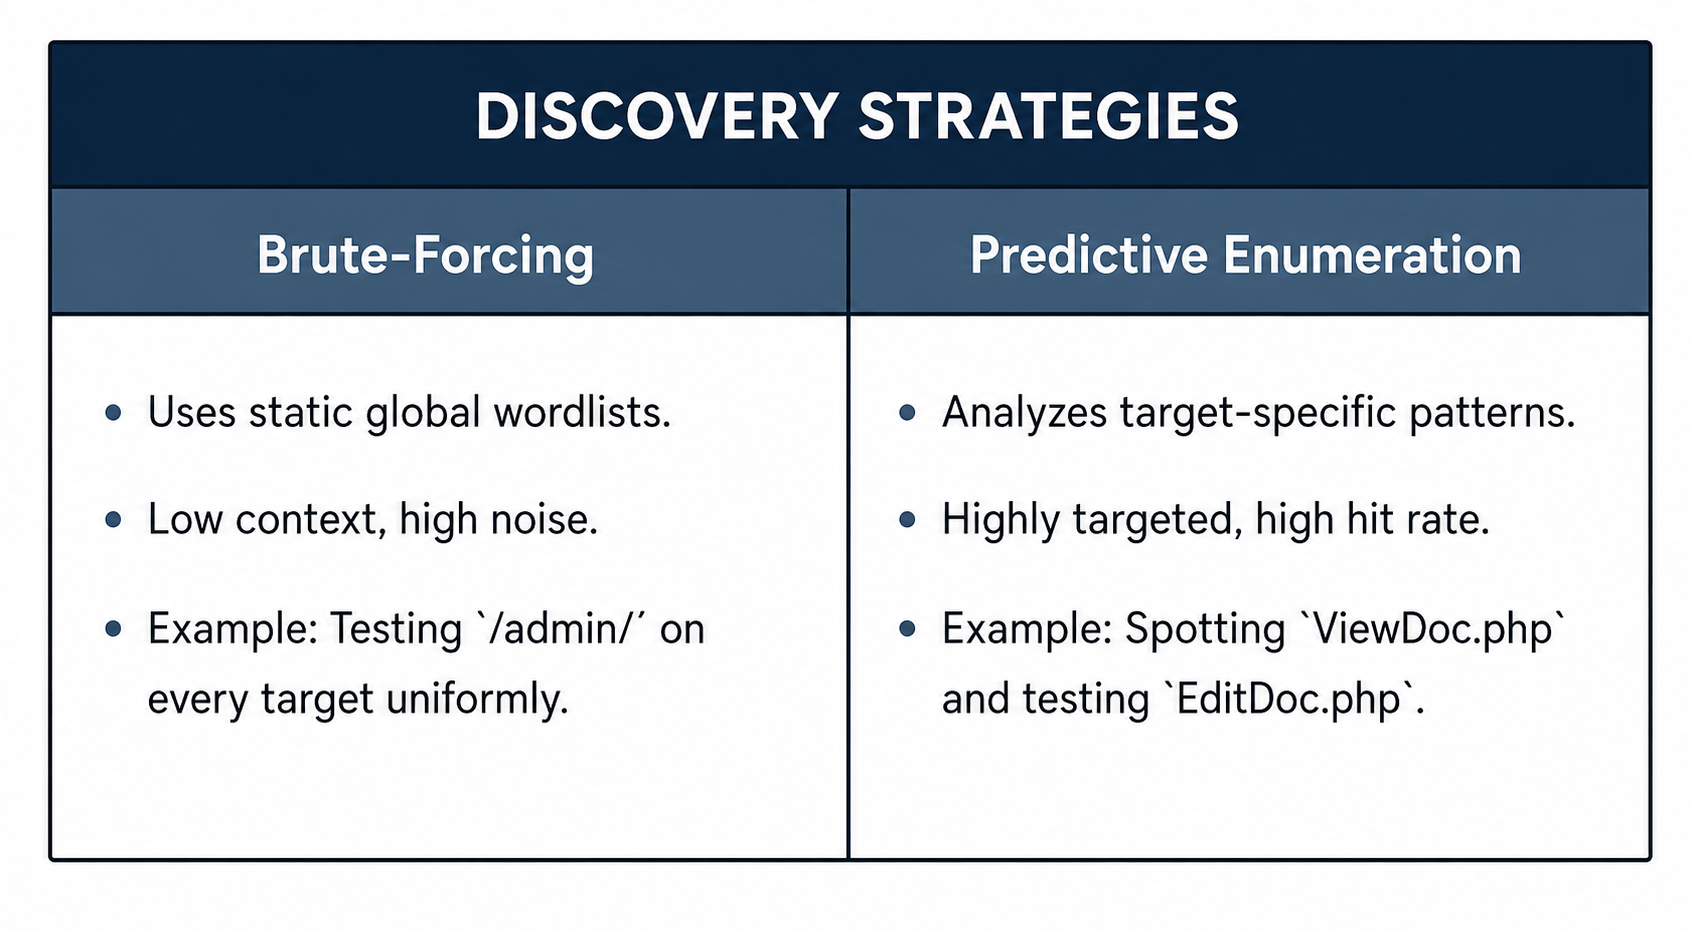
4. Brute-Force vs. Predictive Discovery (Comparison)
5. Pattern-Based Discovery: Building Custom Attack Lists
Instead of relying solely on generic wordlists, this technique analyzes the application's unique naming conventions to construct high-probability attack vectors.
Matrix 1: Action-Object Permutations
If a discovered endpoint is GetInvoice.php:
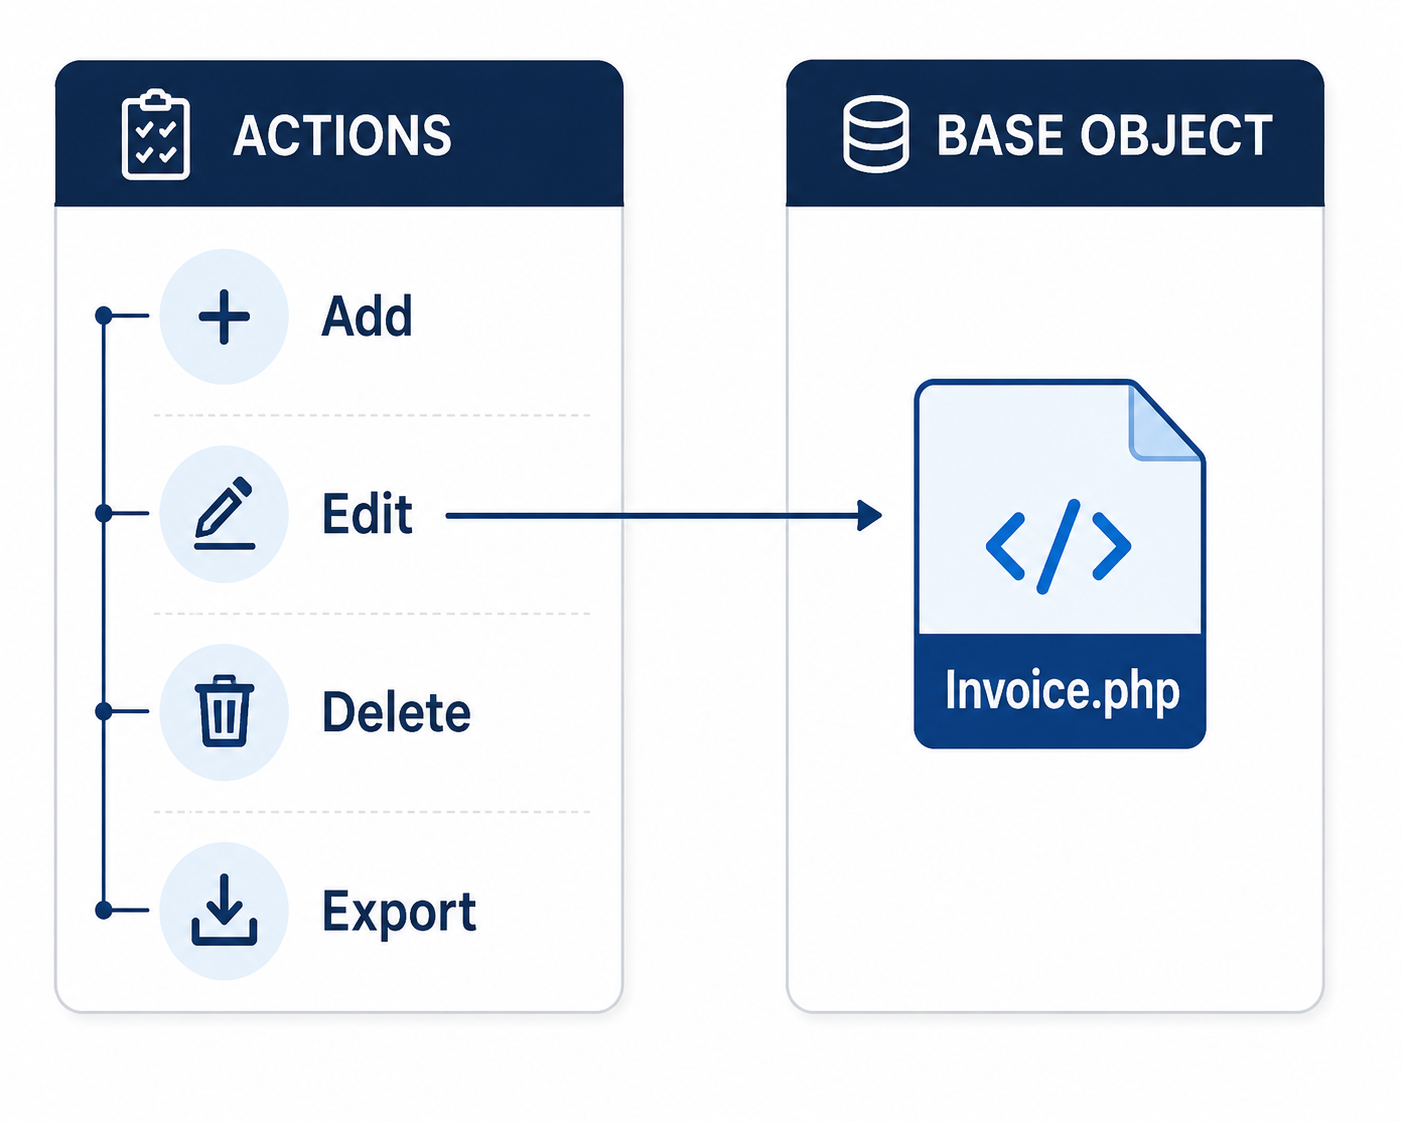
Generated Attack Vectors: AddInvoice.php, EditInvoice.php, DeleteInvoice.php, ExportInvoice.php.
Matrix 2: Contextual Mutations
Case Sensitivity Matching: If the application enforces CamelCase (e.g.,
/UserRole/), test/AdminRole/instead of a generic lowercase/admin/.Sequence Extrapolation:
Endpoint:
/api/v1/download/2023/\(\rightarrow\) Test:/api/v1/download/2024/,/api/v0/Media ID:
/assets/img_101.jpg\(\rightarrow\) Test Range:img_100toimg_120.
6. Client-Side Asset Inspection Workflow
Analyze client-side assets to uncover hidden server-side routes and functionality:
DOM & HTML Inspection:
Hidden input parameters (
<input type="hidden" name="debug" value="true">).Developer HTML comments (
<!-- TODO: Remove staging link /stage-login -->).
JavaScript File Reverse-Engineering:
Extract API routes embedded within JS bundles (
/api/internal/v1/).Identify unlinked UI components or feature flags disabled for low-privilege roles.
Combinatorial Generator Logic:
Target Path:
/auth/Stems:
[login, profile, config]Extensions:
[.php, .php.bak, .inc]Combinations:
/auth/profile.inc,/auth/config.php.bak
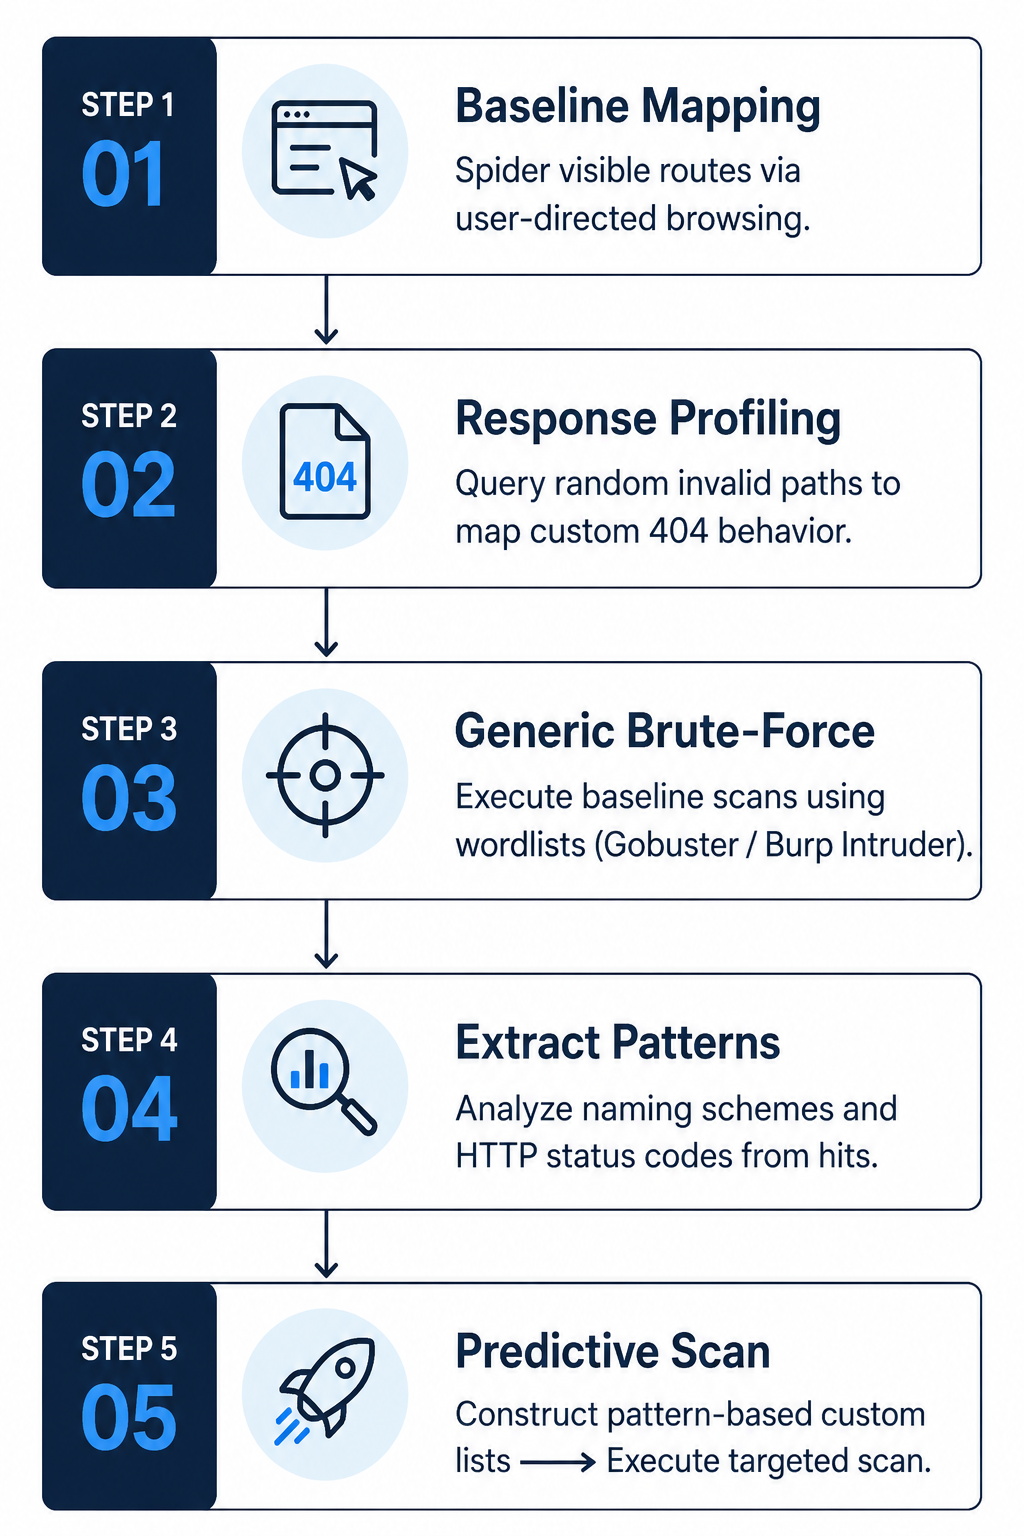
7. Step-by-Step Execution Workflow (Recursive Cycle)
Terminology Reference
Brute-Force Discovery: Using pre-built or static global wordlists to locate unlinked directories and files.
Predictive Enumeration / Pattern-Based Discovery: Decoding existing structural patterns within an application to make intelligent, high-probability guesses for hidden content discovery.